

[May 19, 2024] CAS-004 Exam Dumps - CompTIA Practice Test Questions
New Real CAS-004 Exam Dumps Questions
The CASP+ certification is recognized globally and is highly regarded by employers in the IT industry. Achieving this certification demonstrates that the candidate has advanced-level security knowledge and skills and is capable of designing and implementing secure solutions in complex enterprise environments. CompTIA Advanced Security Practitioner (CASP+) Exam certification is ideal for those who aspire to advance their careers in IT security and want to demonstrate their expertise in enterprise security, risk management, research and analysis, and integration of computing, communications, and business disciplines.
For more information about the CompTIA CAS-004 Exam visit the following reference link:
CompTIA CAS-004 Exam's Reference link
What is the exam cost of CompTIA CAS-004 Exam Certification
The exam cost of CompTIA CAS-004 Exam Certification is $466 USD.
NEW QUESTION # 56
A user from the sales department opened a suspicious file attachment. The sales department then contacted the SOC to investigate a number of unresponsive systems, and the team successfully identified the file and the origin of the attack.
Which of the following is the NEXT step of the incident response plan?
- A. Response
- B. Recovery
- C. Remediation
- D. Containment
Answer: D
NEW QUESTION # 57
An organization recently experienced a ransomware attack. The security team leader is concerned about the attack reoccurring. However, no further security measures have been implemented. Which of the following processes can be used to identify potential prevention recommendations?
- A. Preparation
- B. Detection
- C. Recovery
- D. Remediation
Answer: A
Explanation:
No further security measures have been implemented, so an incident response plan must be addressed. Preparation is the step 1 of this process.
NEW QUESTION # 58
A threat hunting team receives a report about possible APT activity in the network. Which of the following threat management frameworks should the team implement?
- A. The Diamond Model of Intrusion Analysis
- B. MITRE ATT&CK
- C. The Cyber Kill Chain
- D. NIST SP 800-53
Answer: B
Explanation:
MITRE ATT&CK is the right answer, Cyber kill chain doesn't hand persistent as specific case since in chain event persistence is part of it. Review the link below for side by side comparison and also talks about how MITRE handles persistence attacks (search for the word).
https://verveindustrial.com/resources/blog/what-is-mitre-attack-framework/
NEW QUESTION # 59
Which of the following allows computation and analysis of data within a ciphertext without knowledge of the plaintext?
- A. Homomorphic encryption
- B. Asymmetric cryptography
- C. Lattice-based cryptography
- D. Quantum computing
Answer: A
NEW QUESTION # 60
A mobile application developer is creating a global, highly scalable, secure chat application. The developer would like to ensure the application is not susceptible to on-path attacks while the user is traveling in potentially hostile regions. Which of the following would BEST achieve that goal?
- A. Configure certificate pinning inside the application.
- B. Utilize the SAN certificate to enable a single certificate for all regions.
- C. Enable HSTS on the application's server side for all communication.
- D. Deploy client certificates to all devices in the network.
Answer: A
Explanation:
Explanation
Certificate pinning is a technique that embeds one or more trusted certificates or public keys inside an application, and verifies that any certificate presented by a server matches one of those certificates or public keys. Certificate pinning can prevent on-path attacks, such as man-in-the-middle (MITM) attacks, which intercept and modify the communication between a client and a server.
Configuring certificate pinning inside the application would allow the mobile application developer to create a global, highly scalable, secure chat application that is not susceptible to on-path attacks while the user is traveling in potentially hostile regions, because it would:
Ensure that only trusted servers can communicate with the application, by rejecting any server certificate that does not match one of the pinned certificates or public keys.
Protect the confidentiality, integrity, and authenticity of the chat messages, by preventing any attacker from intercepting, modifying, or impersonating them.
Enhance the security of the application by reducing its reliance on external factors, such as certificate authorities (CAs), certificate revocation lists (CRLs), or online certificate status protocol (OCSP).
NEW QUESTION # 61
A security engineer needs to recommend a solution that will meet the following requirements:
Identify sensitive data in the provider's network
Maintain compliance with company and regulatory guidelines
Detect and respond to insider threats, privileged user threats, and compromised accounts Enforce datacentric security, such as encryption, tokenization, and access control Which of the following solutions should the security engineer recommend to address these requirements?
- A. DLP
- B. CASB
- C. SWG
- D. WAF
Answer: B
Explanation:
https://www.mcafee.com/enterprise/en-us/security-awareness/cloud/what-is-a-casb.html
NEW QUESTION # 62
A security analyst discovered that the company's WAF was not properly configured. The main web server was breached, and the following payload was found in one of the malicious requests:
Which of the following would BEST mitigate this vulnerability?
- A. CAPTCHA
- B. Data encoding
- C. Input validation
- D. Network intrusion prevention
Answer: C
NEW QUESTION # 63
A security review of the architecture for an application migration was recently completed. The following observations were made:
* External inbound access is blocked.
* A large amount of storage is available.
* Memory and CPU usage are low.
* The load balancer has only a single server assigned.
* Multiple APIs are integrated.
Which of the following needs to be addressed?
- A. Automation
- B. Availability
- C. Performance
- D. Scalability
Answer: D
Explanation:
The observation that the load balancer has only a single server assigned suggests an issue with scalability. Scalability refers to the ability of the system to handle increasing loads by adding resources. In this case, having a single server assigned to a load balancer may not be adequate to handle increased traffic or load, which could lead to performance issues.
NEW QUESTION # 64
A penetration tester obtained root access on a Windows server and, according to the rules of engagement, is permitted to perform post-exploitation for persistence.
Which of the following techniques would BEST support this?
- A. Creating a backdoor
- B. Configuring systemd services to run automatically at startup
- C. Moving laterally to a more authoritative server/service
- D. Exploiting an arbitrary code execution exploit
Answer: A
NEW QUESTION # 65
An organization recently recovered from an attack that featured an adversary injecting Malicious logic into OS bootloaders on endpoint devices Therefore, the organization decided to require the use of TPM for measured boot and attestation, monitoring each component from the IJEFI through the full loading of OS components. of the following TPM structures enables this storage functionality?
- A. Endorsement tickets
- B. Clock/counter structures
- C. Platform configuration registers
- D. Command tag structures with MAC schemes
Answer: C
Explanation:
TPMs provide the ability to store measurements of code and data that can be used to ensure that code and data remain unchanged over time. This is done through Platform Configuration Registers (PCRs), which are structures used to store measurements of code and data. The measurements are taken during the boot process and can be used to compare the state of the system at different times, which can be used to detect any changes to the system and verify that the system has not been tampered with.
NEW QUESTION # 66
Designing a system in which only information that is essential for a particular job task is allowed to be viewed can be accomplished successfully by using:
- A. job rotations
- B. separation of duties
- C. discretionary access
- D. role-based access control
- E. mandatory vacations.
Answer: D
NEW QUESTION # 67
A security architect updated the security policy to require a proper way to verify that packets received between two parties have not been tampered with and the connection remains private. Which of the following cryptographic techniques can be used to ensure the security policy is being enforced properly?
- A. PBKDF2
- B. HMAC SHA256
- C. MD5-based envelope method
- D. PGP
Answer: B
Explanation:
The company should use HMAC SHA256 as a cryptographic technique to ensure that packets received between two parties have not been tampered with and the connection remains private. HMAC stands for hash-based message authentication code, which is a method of generating a message authentication code using a cryptographic hash function and a secret key. HMAC can provide both integrity and authenticity of the packets, as well as resistance to replay attacks. SHA256 is a specific hash function that produces a 256-bit output. SHA256 is considered secure and widely used in various cryptographic applications. Verified References:
https://www.ericsson.com/en/blog/2021/7/cryptography-and-privacy-protecting-private-data
https://www.mdpi.com/journal/cryptography/special_issues/Preserve_Enhance_Privacy
https://link.springer.com/article/10.1007/s11432-021-3393-x
NEW QUESTION # 68
During a recent security incident investigation, a security analyst mistakenly turned off the infected machine prior to consulting with a forensic analyst. upon rebooting the machine, a malicious script that was running as a background process was no longer present. As a result, potentially useful evidence was lost. Which of the following should the security analyst have followed?
- A. Verification
- B. Order of volatility
- C. Chain of custody
- D. Secure storage
Answer: B
Explanation:
Order of volatility is a procedure that a computer forensics examiner must follow during evidence collection. It refers to the order in which digital evidence is collected, starting with the most volatile and moving to the least volatile. Volatile data is data that is not permanent and is easily lost, such as data in memory when you turn off a computer. The security analyst should have followed the order of volatility to preserve the most fragile evidence first, such as the malicious script running as a background process, before turning off the infected machine. Verified Reference:
https://www.computer-forensics-recruiter.com/order-of-volatility/
https://www.sans.org/blog/best-practices-in-digital-evidence-collection/
https://blogs.getcertifiedgetahead.com/order-of-volatility/
NEW QUESTION # 69
A security analyst receives an alert from the SIEM regarding unusual activity on an authorized public SSH jump server. To further investigate, the analyst pulls the event logs directly from /var/log/auth.log:
graphic.ssh_auth_log.
Which of the following actions would BEST address the potential risks by the activity in the logs?
- A. Alerting the misconfigured service account password
- B. Modifying the AllowUsers configuration directive
- C. Restricting external port 22 access
- D. Implementing host-key preferences
Answer: B
NEW QUESTION # 70
A systems administrator at a web-hosting provider has been tasked with renewing the public certificates of all customer sites. Which of the following would BEST support multiple domain names while minimizing the amount of certificates needed?
- A. SAN
- B. CRL
- C. CA
- D. ocsp
Answer: A
Explanation:
The administrator should use SAN certificates to support multiple domain names while minimizing the amount of certificates needed. SAN stands for Subject Alternative Name, which is an extension of a certificate that allows it to include multiple fully-qualified domain names (FQDNs) within the same certificate. For example, a SAN certificate can secure www.example.com, www.example.net, and mail.example.org with one certificate. SAN certificates can reduce the cost and complexity of managing multiple certificates for different domains. SAN certificates can also support wildcard domains, such as *.example.com, which can cover any subdomain under that domain. Verified References:
https://www.techtarget.com/searchsecurity/definition/Subject-Alternative-Name
https://www.techtarget.com/searchsecurity/definition/wildcard-certificate
https://www.nexcess.net/help/what-is-a-multi-domain-ssl-certificate/
NEW QUESTION # 71
A business stores personal client data of individuals residing in the EU in order to process requests for mortgage loan approvals.
Which of the following does the business's IT manager need to consider?
- A. The language of the web application
- B. The availability of personal data
- C. The company's annual revenue
- D. The right to personal data erasure
Answer: D
Explanation:
Reference:
The right to personal data erasure, also known as the right to be forgotten, is one of the requirements of the EU General Data Protection Regulation (GDPR), which applies to any business that stores personal data of individuals residing in the EU. This right allows individuals to request the deletion of their personal data from a business under certain circumstances. The availability of personal data, the company's annual revenue, and the language of the web application are not relevant to the GDPR. Verified Reference: https://www.comptia.org/blog/what-is-gdpr https://partners.comptia.org/docs/default-source/resources/casp-content-guide
NEW QUESTION # 72
An engineering team has deployed a new VPN service that requires client certificates to be used in order to successfully connect. On iOS devices, however, the following error occurs after importing the .p12 certificate file:
mbedTLS: ca certificate is undefined
Which of the following is the root cause of this issue?
- A. OpenSSL is not configured to support PKCS#12 certificate files.
- B. The VPN client configuration is missing the CA private key.
- C. iOS devices have an empty root certificate chain by default.
- D. The iOS keychain imported only the client public and private keys.
Answer: D
NEW QUESTION # 73
A company's finance department acquired a new payment system that exports data to an unencrypted file on the system. The company implemented controls on the file so only appropriate personnel are allowed access.
Which of the following risk techniques did the department use in this situation?
- A. Avoid
- B. Transfer
- C. Accept
- D. Mitigate
Answer: D
NEW QUESTION # 74
A major broadcasting company that requires continuous availability to streaming content needs to be resilient against DDoS attacks Which of the following is the MOST important infrastructure security design element to prevent an outage7
- A. Leveraging content delivery network across multiple regions
- B. Scaling horizontally to handle increases in traffic
- C. Ensuring cloud autoscaling is in place
- D. Supporting heterogeneous architecture
Answer: A
Explanation:
Explanation
A content delivery network (CDN) is a distributed system of servers that delivers web content to users based on their geographic location, the origin of the content, and the performance of the network. A CDN can help improve the availability and performance of web applications by caching content closer to the users, reducing latency and bandwidth consumption. A CDN can also help mitigate distributed denial-of-service (DDoS) attacks by absorbing or filtering malicious traffic before it reaches the origin servers, reducing the impact on the application availability. Supporting heterogeneous architecture means using different types of hardware, software, or platforms in an IT environment. This can help improve resilience by reducing single points of failure and increasing compatibility, but it does not directly prevent DDoS attacks. Ensuring cloud autoscaling is in place means using cloud services that automatically adjust the amount of resources allocated to an application based on the demand or load. This can help improve scalability and performance by providing more resources when needed, but it does not directly prevent DDoS attacks. Scaling horizontally means adding more servers or nodes to an IT environment to increase its capacity or throughput. This can help improve scalability and performance by distributing the load across multiple servers, but it does not directly prevent DDoS attacks. References: [CompTIA Advanced Security Practitioner (CASP+) Certification Exam Objectives], Domain 2: Enterprise Security Architecture, Objective 2.4: Select controls based on systems security evaluation models
NEW QUESTION # 75
A security analyst is reviewing the following output:
Which of the following would BEST mitigate this type of attack?
- A. Placing a WAF inline
- B. Deploying a honeypot
- C. Implementing an IDS
- D. Installing a network firewall
Answer: A
NEW QUESTION # 76
A company makes consumer health devices and needs to maintain strict confidentiality of unreleased product designs.
Recently unauthorized photos of products still in development have been for sale on the dark web.
The Chief Information Security Officer (CISO) suspects an insider threat, but the team that uses the secret outdoor testing area has been vetted many times and nothing suspicious has been found.
Which of the following is the MOST likely cause of the unauthorized photos?
- A. The location of the testing facility was discovered by analyzing fitness device information the test engineers posted on a website
- B. The company failed to implement least privilege on network devices, and a hacktivist published stolen public relations photos
- C. Pre-release marketing materials for a single device were accidentally left in a public location
- D. One of the test engineers is working for a competitor and covertly installed a RAT on the marketing department's servers
Answer: C
NEW QUESTION # 77
In a shared responsibility model for PaaS, which of the following is a customer's responsibility?
- A. Physical security
- B. Host infrastructure
- C. OS security
- D. Network security
Answer: C
Explanation:
In a shared responsibility model for PaaS, the customer's responsibility is OS security. PaaS stands for Platform as a Service, which is a cloud service model that provides a platform for customers to develop, run, and manage applications without having to deal with the underlying infrastructure. The cloud provider is responsible for the physical security, network security, and host infrastructure of the platform, while the customer is responsible for the security of the operating system, the application, and the data. The customer needs to ensure that the operating system is patched, configured, and protected from malware and unauthorized access. Verified Reference:
https://learn.microsoft.com/en-us/azure/security/fundamentals/shared-responsibility
https://www.techtarget.com/searchcloudcomputing/feature/The-cloud-shared-responsibility-model-for-IaaS-PaaS-and-SaaS
https://www.splunk.com/en_us/blog/learn/shared-responsibility-model.html
NEW QUESTION # 78
In preparation for the holiday season, a company redesigned the system that manages retail sales and moved it to a cloud service provider. The new infrastructure did not meet the company's availability requirements. During a postmortem analysis, the following issues were highlighted:
1. International users reported latency when images on the web page were initially loading.
2. During times of report processing, users reported issues with inventory when attempting to place orders.
3. Despite the fact that ten new API servers were added, the load across servers was heavy at peak times.
Which of the following infrastructure design changes would be BEST for the organization to implement to avoid these issues in the future?
- A. Serve images from an object storage bucket with infrequent read times, replicate the database across different regions, and dynamically create API servers based on load.
- B. Serve static-content object storage across different regions, increase the instance size on the managed relational database, and distribute the ten API servers across multiple regions.
- C. Serve static content via distributed CDNs, create a read replica of the central database and pull reports from there, and auto-scale API servers based on performance.
- D. Increase the bandwidth for the server that delivers images, use a CDN, change the database to a non-relational database, and split the ten API servers across two load balancers.
Answer: C
NEW QUESTION # 79
A security analyst is reviewing the following vulnerability assessment report: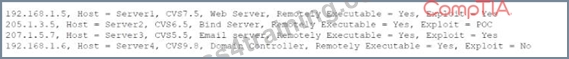
Which of the following should be patched FIRST to minimize attacks against Internet-facing hosts?
- A. Servers
- B. Server1
- C. Server2
- D. Server 3
Answer: B
NEW QUESTION # 80
A financial services company wants to migrate its email services from on-premises servers to a cloud-based email solution. The Chief information Security Officer (CISO) must brief board of directors on the potential security concerns related to this migration. The board is concerned about the following.
* Transactions being required by unauthorized individual
* Complete discretion regarding client names, account numbers, and investment information.
* Malicious attacker using email to distribute malware and ransom ware.
* Exfiltration of sensitivity company information.
The cloud-based email solution will provide an6-malware, reputation-based scanning, signature-based scanning, and sandboxing. Which of the following is the BEST option to resolve the board's concerns for this email migration?
- A. SSL VPN
- B. Endpoint detection response
- C. Data loss prevention
- D. Application whitelisting
Answer: C
NEW QUESTION # 81
......
CAS-004 Certification Exam Dumps Questions in here: https://drive.google.com/open?id=1v3QMYW1eHb8XSw5L2nsaOCU8jhUywiFF
Pass Your CAS-004 Exam Easily with Accurate PDF Questions: https://www.pass4training.com/CAS-004-pass-exam-training.html
