

Practice with MS-100 Dumps for Microsoft 365 Certified Exam Questions & Answer
REAL MS-100 Exam Questions With 100% Refund Guarantee
How You Can Level-up Your Career Further?
Passing the Microsoft MS-100 exam helps one become an Enterprise expert. Hierarchy-wise, this is the highest certification that one can earn related to Microsoft 365. However, you can explore other areas of expertise like Azure and Windows to level-up the career.
Microsoft has a lot to offer. Just pass this exam and have endless opportunities afterward.
NEW QUESTION 221
Your network contains an on premises Active Directory domain named contoso.com. The domain contains five domain controllers.
Your company purchases Microsoft 365 and creates a Microsoft Azure Active Directory (Azure AD) tenant named contoso.onmicrosoft.com.
You plan to establish federation authentication between on premises Active Directory and the Azure AD tenant by using Active Directory Federation Services (AD FS).
You need to establish the federation.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point
Answer:
Explanation:
Explanation
The on-premises Active Directory domain is named contoso.com. Before you can configure federation authentication between on-premises Active Directory and the Azure AD tenant, you need to add the domain contoso.com to Microsoft 365. You do this by adding a custom domain name.
The next step is to establish the federation. You can configure AD FS by using Azure AD Connect.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/hybrid/how-to-connect-install-custom#configuring-feder
NEW QUESTION 222
You are developing a single-page application (SPA) that authenticates users by using MSALjs. The SPA must meet the following requirements:
* Only allow access to the users in an organization named contoso.onmicrosoft.com.
* Support single sign-on (SSO) across tabs and user sessions.
How should you complete the code for the SPA? To answer, select the appropriate options in the answer are a. NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 223
You have a Microsoft 365 subscription.
You need to implement Windows Defender Advanced Threat Protection (ATP) for all the supported devices enrolled devices enrolled on mobile device management (MDM).
What should you include in the device configuration profile? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/intune/advanced-threat-protection
NEW QUESTION 224
Your network contains an Active Directory domain named contoso.com. The domain contains 1000 Windows
8.1 devices.
You plan to deploy a custom Windows 10 Enterprise image to the Windows 8.1 devices.
You need to recommend a Windows 10 deployment method.
What should you recommend?
- A. an in-place upgrade
- B. Wipe and load refresh
- C. Windows Autopilot
- D. a provisioning package
Answer: B
Explanation:
To deploy a custom image, you must use the wipe and load refresh method. You cannot deploy a custom image by using an in-place upgrade, Windows Autopilot or a provisioning package.
Reference:
https://docs.microsoft.com/en-us/windows/deployment/windows-10-deployment-scenarios
NEW QUESTION 225
Your company has a hybrid deployment of Microsoft 365.
An on-premises user named User1 is synced to Microsoft Azure Active Directory (Azure AD).
Azure AD Connect is configured as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
User1 cannot change her password from any Microsoft portals because Password Writeback is disabled in the Azure AD Connect configuration.
If the password for User1 is changed in Active Directory, the password will be synchronized to Azure AD because Password Synchronization is enabled in the Azure AD Connect configuration.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/hybrid/how-to-connect-install-custom
NEW QUESTION 226
You need to meet the application requirement for the Office 365 ProPlus applications.
You create a XML file that contains the following settings.
Use the drop-down menus to select the choice that complete each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 227
Your network contains three Active Directory forests.
You create a Microsoft Azure Active Directory (Azure AD) tenant.
You plan to sync the on premises Active Directory (Azure AD).
You need to recommend a synchronization solution. The solution must ensure that the synchronization can complete successfully and as quickly as possible if a single server fails.
What should you include in the recommendation?
- A. six Azure AD Connect sync servers and three Azure AD Connect sync servers in staging mode
- B. Three Azure AD Connect sync servers and three Azure AD Connect sync servers in staging mode
- C. Three Azure AD Connect sync servers and one Azure AD Connect sync servers in staging mode
- D. One Azure AD Connect sync servers one Azure AD Connect sync servers in staging mode
Answer: D
Explanation:
Azure AD Connect can be active on only one server. You can install Azure AD Connect on another server for redundancy but the additional installation would need to be in Staging mode. An Azure AD connect installation in Staging mode is configured and ready to go but it needs to be manually switched to Active to perform directory synchronization.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/hybrid/how-to-connect-install-custom
NEW QUESTION 228
Your network contains an Active Directory domain named fabrikam.com. The domain contains the objects shown in the following table.
The group have the members shown in the following table.
You are configure synchronization between fabrikam.com and a Microsoft Azure Active Director (Azure AD) tenant.
You configure the domain/OU Filtering settings in Azure AD Connect as shown in the Domain>OU Filtering exhibit. (Click the Domain/OU Filtering tab.) You configure the Filtering in Azure Connect as shown in the Filtering exhibit. (Click the Filtering tab.) NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Box 1: No
The filtering is configured to synchronize Group2 and OU2 only. The effect of this is that only members of Group2 who are in OU2 will be synchronized.
User2 is in Group2. However, the User2 account object is in OU1 so User2 will not synchronize to Azure AD.
Box 2: Yes
Group2 is in OU2 so Group2 will synchronize to Azure AD. However, only members of the group who are in OU2 will synchronize. Members of Group2 who are in OU1 will not synchronize.
Box 3: Yes
User3 is in Group2 and in OU2. Therefore, User3 will synchronize to Azure AD.
References:
https://docs.microsoft.com/en-us/azure/active-directory/hybrid/how-to-connect-sync-configure-filtering#group-b
NEW QUESTION 229
You have a Microsoft Azure Active Directory (Azure AD) tenant named contoso.com.
You have three applications App1, App2, App3. The Apps use files that have the same file extensions.
Your company uses Windows Information Protection (WIP). WIP has the following configurations:
* Windows Information Protection mode: Silent
* Protected apps: App1
* Exempt apps: App2
From App1, you create a file named File1.
What is the effect of the configurations? To answer, select the appropriate options in the answer area.
Answer:
Explanation:
Explanation
Reference:
https://docs.microsoft.com/en-us/windows/security/information-protection/windows-information-protection/crea
https://docs.microsoft.com/en-us/windows/security/information-protection/windows-information-protection/crea
NEW QUESTION 230
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an Active Directory domain named contoso.com that is synced to Microsoft Azure Active Directory (Azure AD).
You manage Windows 10 devices by using Microsoft System Center Configuration Manager (Current Branch).
You configure a pilot for co-management.
You add a new device named Device1 to the domain. You install the Configuration Manager client on Device1.
You need to ensure that you can manage Device1 by using Microsoft Intune and Configuration Manager.
Solution: You add Device1 to an Active Directory group.
Does this meet the goal?
- A. Yes
- B. No
Answer: B
Explanation:
Device1 has the Configuration Manager client installed so you can manage Device1 by using Configuration Manager.
To manage Device1 by using Microsoft Intune, the device has to be enrolled in Microsoft Intune. In the Co-management Pilot configuration, you configure a Configuration Manager Device Collection that determines which devices are auto-enrolled in Microsoft Intune. You need to add Device1 to the Device Collection, not an Active Directory Group. Therefore, this solution does not meet the requirements.
Reference:
https://docs.microsoft.com/en-us/configmgr/comanage/how-to-enable
NEW QUESTION 231
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 subscription.
You discover that some external users accessed content on a Microsoft SharePoint site. You modify the SharePoint sharing policy to prevent sharing outside your organization.
You need to be notified if the SharePoint policy is modified in the future.
Solution: From the Security & Compliance admin center, you create a threat management policy.
Does this meet the goal?
- A. Yes
- B. No
Answer: A
Explanation:
Section: [none]
Explanation:
We can create a threat management policy to alert us when the sharing policy is changed.
Create a new Alert policy > under Category select Threat Management > under 'Activity is' scroll down to the
'Site administration activities' and select 'Changed a sharing policy'.
NEW QUESTION 232
Your network contains an Active Directory domain and a Microsoft Azure Active Directory (Azure AD) tenant.
You implement directory synchronization for all 10.000 users in the organization.
You automate the creation of 100 new user accounts.
You need to ensure that the new user accounts synchronize to Azure AD as quickly as possible Which command should you run? To answer, select the appropriate options in the answer area.
NOTE: Each correct select ion is worth one point.
Answer:
Explanation:
NEW QUESTION 233
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your company has a Microsoft Office 365 tenant.
You suspect that several Office 365 features were recently updated.
You need to view a list of the features that were recently updated in the tenant.
Solution: You use Dashboard in Security & Compliance.
Does this meet the goal?
- A. Yes
- B. No
Answer: B
Explanation:
Section: [none]
Explanation:
Depending on what your organization's Office 365 subscription includes, the Dashboard in Security & Compliance includes several widgets, such as Threat Management Summary, Threat Protection Status, Global Weekly Threat Detections, Malware, etc. It does not display a list of the features that were recently updated in the tenant so this solution does not meet the goal.
To meet the goal, you need to use Message center in the Microsoft 365 admin center.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/office-365-security/security-dashboard
https://docs.microsoft.com/en-us/office365/admin/manage/message-center?view=o365-worldwide
NEW QUESTION 234
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your company plans to deploy several Microsoft Office 365 services.
You need to design an authentication strategy for the planned deployment. The solution must meet the following requirements:
* Users must be able to authenticate during business hours only.
* Authentication requests must be processed successfully if a single server fails.
* When the password for an on-premises user account expires, the new password must be enforced the next time the user signs in.
* Users who connect to Office 365 services from domain-joined devices that are connected to the internal network must be signed in automatically.
Solution: You design an authentication strategy that uses federation authentication by using Active Directory Federation Services (AD FS). The solution contains two AD FS servers and two Web Application Proxies.
Does this meet the goal?
- A. Yes
- B. No
Answer: B
Explanation:
Section: [none]
Explanation:
This solution meets the following requirements:
* Users must be able to authenticate during business hours only.
* Authentication requests must be processed successfully if a single server fails.
* When the password for an on-premises user account expires, the new password must be enforced the next time the user signs in.
The following requirement is not met:
* Users who connect to Office 365 services from domain-joined devices that are connected to the internal network must be signed in automatically.
To meet this requirement, you would need to configure seamless Single Sign-on (SSO) Reference:
https://docs.microsoft.com/en-us/azure/security/azure-ad-choose-authn
NEW QUESTION 235
You have a new Microsoft 365 subscription.
A user named User1 has a mailbox in Microsoft Exchange Online.
You need to log any changes to the mailbox folder permissions of User1.
Which command should you run? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
To enable auditing for a single mailbox (in this example, belonging to Holly Sharp), use this PowerShell command: Set-Mailbox username -AuditEnabled $true References:
https://support.microsoft.com/en-us/help/4026501/office-auditing-in-office-365-for-admins
https://docs.microsoft.com/en-us/powershell/module/exchange/mailboxes/set-mailbox?view=exchange-ps
NEW QUESTION 236
Your network contains an on-premises Active Directory domain. The domain contains the users shown in the following table.
You have a Microsoft 365 subscription that is linked to an Azure Active Directory (Azure AD) tenant named contoso.com. You configure Azure AD Connect to sync the on-premises domain to contoso.com as shown in the following exhibit.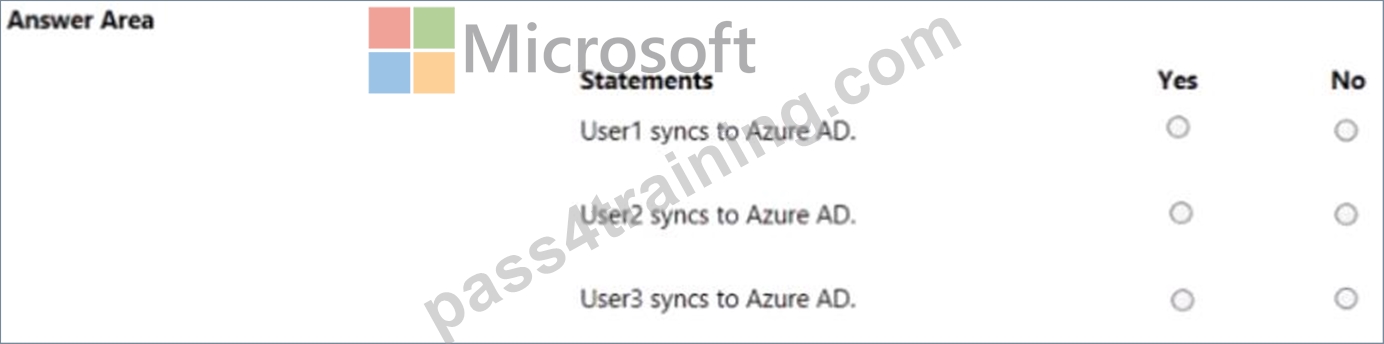
Answer:
Explanation:
NEW QUESTION 237
......
PDF Download Microsoft Test To Gain Brilliante Result!: https://www.pass4training.com/MS-100-pass-exam-training.html
Get Special Discount Offer on MS-100 Dumps PDF: https://drive.google.com/open?id=1mfbQ6W1xzEoYHl4mXcKV8C3k1ZBMQ08Y
