

Prepare JN0-230 Question Answers - JN0-230 Exam Dumps
Real Juniper JN0-230 Exam Questions [Updated 2022]
How to Prepare for Juniper Security Associate (JNCIA-SEC) (JN0-230)
Preparation Guide for Juniper Security Associate (JNCIA-SEC) (JN0-230)
Introduction
Juniper 362 Service Provider Routing and Switching Specialist exam is designed for Designed for networking professionals with beginner-intermediate knowledge of the Juniper Networks Junos OS for SRX Series devices, this written exam verifies the candidate's understanding of security technologies and related platform configuration and troubleshooting skills.
The Juniper Security Associate Service Provider Routing and Switching track allows participants to demonstrate competence with Juniper Networks technology. Successful candidates demonstrate thorough understanding of networking technology in general and Juniper Networks service provider routing and switching platforms. This is covered in JN0-362 exam dumps pdf.
this written exam verifies the candidate's basic understanding of routing and switching technologies and related platform configuration and troubleshooting skills. JNCIS-SP exam topics are based on the content of the recommended instructor led training courses, as well as the additional resources.
To earn the certification, the candidate will have to:
- Spanning-Tree Protocols
- IPv6
- Protocol-Independent Routing
- Intermediate System to Intermediate System (IS-IS)
- High Availability
- Layer 2 Bridging and VLANs
Pass4training offers you the most updated JN0-362 practice exams and JN0-362 practice exams material so you can start any time. To assess your skill level and to identify gaps in your knowledge, take the practice exam and get comfortable with the material.
Outline of IJSEC Class
The Introduction to Juniper Security (IJSEC) course can be divided into specific sections, with every objective covered on specific days. Find all the details explained below:
Day One
On the first day of your certification training, the instructors will begin by introducing the course. Then, they will go further to cover the concepts of Juniper Connected Security, Juniper Connected Security-SRX Series Devices, Security Objects, and Security Policies. Also, during the first day, you’ll have to perform three labs dealing with Initial Configuration, the Creation of Security Objects, and Executing Security Methods.
NEW QUESTION 27
Exhibit.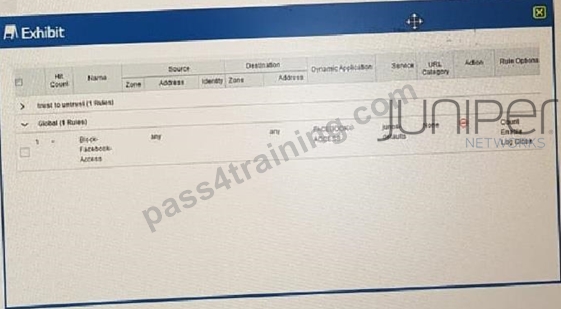
Which two statements are true? (Choose two.)
- A. Logs for this security policy are not generated.
- B. Logs for this security policy are generated.
- C. Traffic statistics for this security policy are generated.
- D. Traffic static for this security policy are not generated.
Answer: B,D
NEW QUESTION 28
What should you configure if you want to translate private source IP address to a single public IP address?
- A. Security Director
- B. Destination NAT
- C. Source NAT
- D. Content filtering
Answer: A
NEW QUESTION 29
Which two statements are correct about using global-based policies over zone-based policies? (Choose two.)
- A. With global-based policies, you do not need to specify a source address in the match criteria.
- B. With global-based policies, you do not need to specify a source zone in the match criteria.
- C. With global-based policies, you do not need to specify a destination address in the match criteria.
- D. With global-based policies, you do not need to specify a destination zone in the match criteria.
Answer: B,D
Explanation:
Explanation/Reference:
NEW QUESTION 30
Which statement about IPsec is correct?
- A. IPsec can provide encryption but not data integrity.
- B. IPsec support packet fragmentation by intermediary devices.
- C. IPsec must use certificates to provide data encryption
- D. IPsec support both tunnel and transport modes.
Answer: D
NEW QUESTION 31
You have configured a Web filtering UTM policy.
Which action must be performed before the Web filtering UTM policy takes effect?
- A. The UTM policy must be linked to an ingress interface.
- B. The UTM policy must be linked to an egress interface.
- C. The UTM policy must be linked to a security policy.
- D. The UTM policy must be configured as a routing next hop.
Answer: C
NEW QUESTION 32
You have configured antispam to allow e-mail from example.com, however the logs you see that [email protected] is blocked Referring to the exhibit.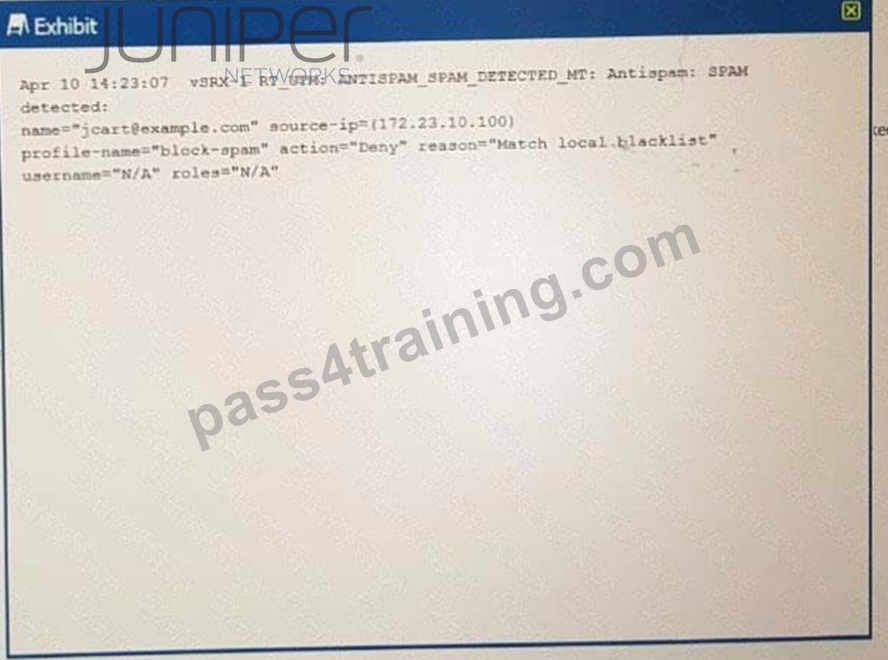
What are two ways to solve this problem?
- A. Delete [email protected] from the profile antispam address whitelist
- B. Add [email protected] to the profile antispam address whitelist.
- C. Verify connectivity with the SBL server.
- D. Delete [email protected] from the profile antispam address blacklist
Answer: B,D
NEW QUESTION 33
Users should not have access to Facebook, however, a recent examination of the logs security show that users are accessing Facebook.
Referring to the exhibit,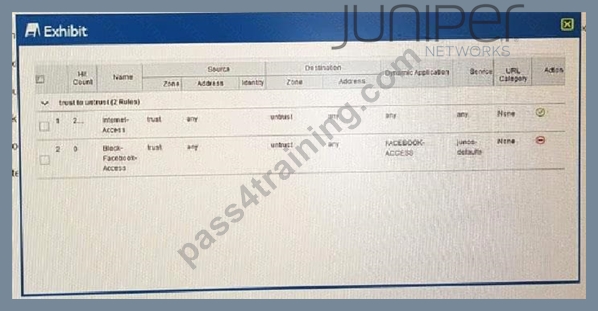
what should you do to solve this problem?
- A. Change the Internet-Access rule from a zone policy to a global policy
- B. Move the Block-Facebook-Access rule from a zone policy to a global policy
- C. Change the source address for the Block-Facebook-Access rule to the prefix of the users
- D. Move the Block-Facebook-Access rule before the Internet-Access rule
Answer: D
NEW QUESTION 34
Which security object defines a source or destination IP address that is used for an employee Workstation?
- A. Address book entry
- B. Screen
- C. scheduler
- D. Zone
Answer: A
NEW QUESTION 35
Which statements is correct about global security policies?
- A. Global policies allow you to regulate traffic with addresses and applications, regardless of their security zones.
- B. Traffic matching global is not added to the session table.
- C. Global security require you to identify a source and destination zone.
- D. Global policies eliminate the need to assign interface to security zones.
Answer: A
NEW QUESTION 36
Which statement is correct about address books for security policies on SRX Series devices?
- A. A zone can only use one address book at a time.
- B. Addresses in the global address book are preferred over addresses in a zone-based address book.
- C. NAT rules can use address objects only from the global address book.
- D. Address sets can contain addresses from different security zones.
Answer: C
Explanation:
Explanation/Reference:
NEW QUESTION 37
What is the correct order of processing when configuring NAT rules and security policies?
- A. Static NAT > destination NAT> policy lookup > source NAT
- B. Source NAT > static NAT > destination NAT > policy lookup
- C. Destination NAT> policy lookup > source NAT> static NAT
- D. Policy lookup > source NAT > static NAT > destination NAT
Answer: D
NEW QUESTION 38
Which two statements are true about the null zone? (Choose two.)
- A. All traffic to the null zone is allowed
- B. All interface belong to the bull zone by default.
- C. All traffic to the null zone is dropped.
- D. The null zone is a user-defined zone
Answer: B,C
NEW QUESTION 39
Which statements is correct about SKY ATP?
- A. Sky ATP only support sending threat feeds to vSRX Series devices
- B. Sky ATP is an open-source security solution.
- C. Sky ATP is a cloud-based security threat analyzer that performs multiple tasks
- D. Sky ATP is used to automatically push out changes to the AppSecure suite.
Answer: C
NEW QUESTION 40
Which two actions are performed on an incoming packet matching an existing session? (Choose two.)
- A. zones processing
- B. screens processing
- C. security policy evaluation
- D. service ALG processing
Answer: B,D
NEW QUESTION 41
Which two statements are true about UTM on an SRX340? (Choose two.)
- A. A default UTM profile is created
- B. No default UTM policy is created
- C. No default profile is created.
- D. A default UTM policy is created.
Answer: A,C
NEW QUESTION 42
You are concerned that unauthorized traffic is using non-standardized ports on your network.
In this scenario, which type of security feature should you implement?
- A. Application firewall
- B. Firewall filters
- C. Sky ATP
- D. Zone-based policies
Answer: A
NEW QUESTION 43
Which two elements are needed on an SRX Series device to set up a remotesyslogserver? (Choose two.)
- A. Data size
- B. Data throughput
- C. Data type
- D. IP address
Answer: A,C
NEW QUESTION 44
By default, revenue interfaces are placed into which system-defined security zone on an SRX Series device?
- A. junos-trust
- B. untrust
- C. trust
- D. null
Answer: D
NEW QUESTION 45
Which two statements are true about the null zone? (Choose two.)
- A. The null zone is a user-defined zone
- B. All traffic to the null zone is allowed
- C. All interface belong to the bull zone by default.
- D. All traffic to the null zone is dropped.
Answer: A,B
NEW QUESTION 46
Which two statements are correct about using global-based policies over zone-based policies? (Choose two.)
- A. With global-based policies, you do not need to specify a source address in the match criteria.
- B. With global-based policies, you do not need to specify a source zone in the match criteria.
- C. With global-based policies, you do not need to specify a destination address in the match criteria.
- D. With global-based policies, you do not need to specify a destination zone in the match criteria.
Answer: B,D
NEW QUESTION 47
Which two segments describes IPsec VPNs? (Choose two.)
- A. IPsec VPNs are dedicated physical connections between two private networks.
- B. IPsec VPNs use security to secure traffic over a public network between two remote sites.
- C. IPsec VPN traffic is always authenticated.
- D. IPsec VPN traffic is always encrypted.
Answer: A,B
NEW QUESTION 48
What must you do first to use the Monitor/Events workspace in the j-Web interface?
- A. You must enable security logging that uses the TLS transport mode.
- B. You must enable event mode security logging on the SRX Series device.
- C. You must enable security logging that uses the SD-Syslog format.
- D. You must enable stream mode security logging on the SRX Series device
Answer: B
NEW QUESTION 49
You configure and applied several global policies and some of the policies have overlapping match criteria.
- A. In this scenario, how are these global policies applies?
- B. The first matched policy is the only policy applied.
- C. The most restrictive that matches is applied.
- D. The least restrictive policy that matches is applied.
Answer: A
NEW QUESTION 50
......
Understanding functional and technical aspects of Protocol-Independent Routing
The following will be discussed in JN0-362 exam dumps:
- Filter-based forwarding
- Filter-based forwarding
- Static, aggregate, and generated routes
- Routing instances, including RIB groups
- Martian addresses
- Load balancing
- Static, aggregate, and generated routes
- Load balancing
- Demonstrate knowledge of how to configure, monitor, or troubleshoot various protocol-independent routing components
JN0-230 Exam Dumps Pass with Updated 2022: https://www.pass4training.com/JN0-230-pass-exam-training.html
